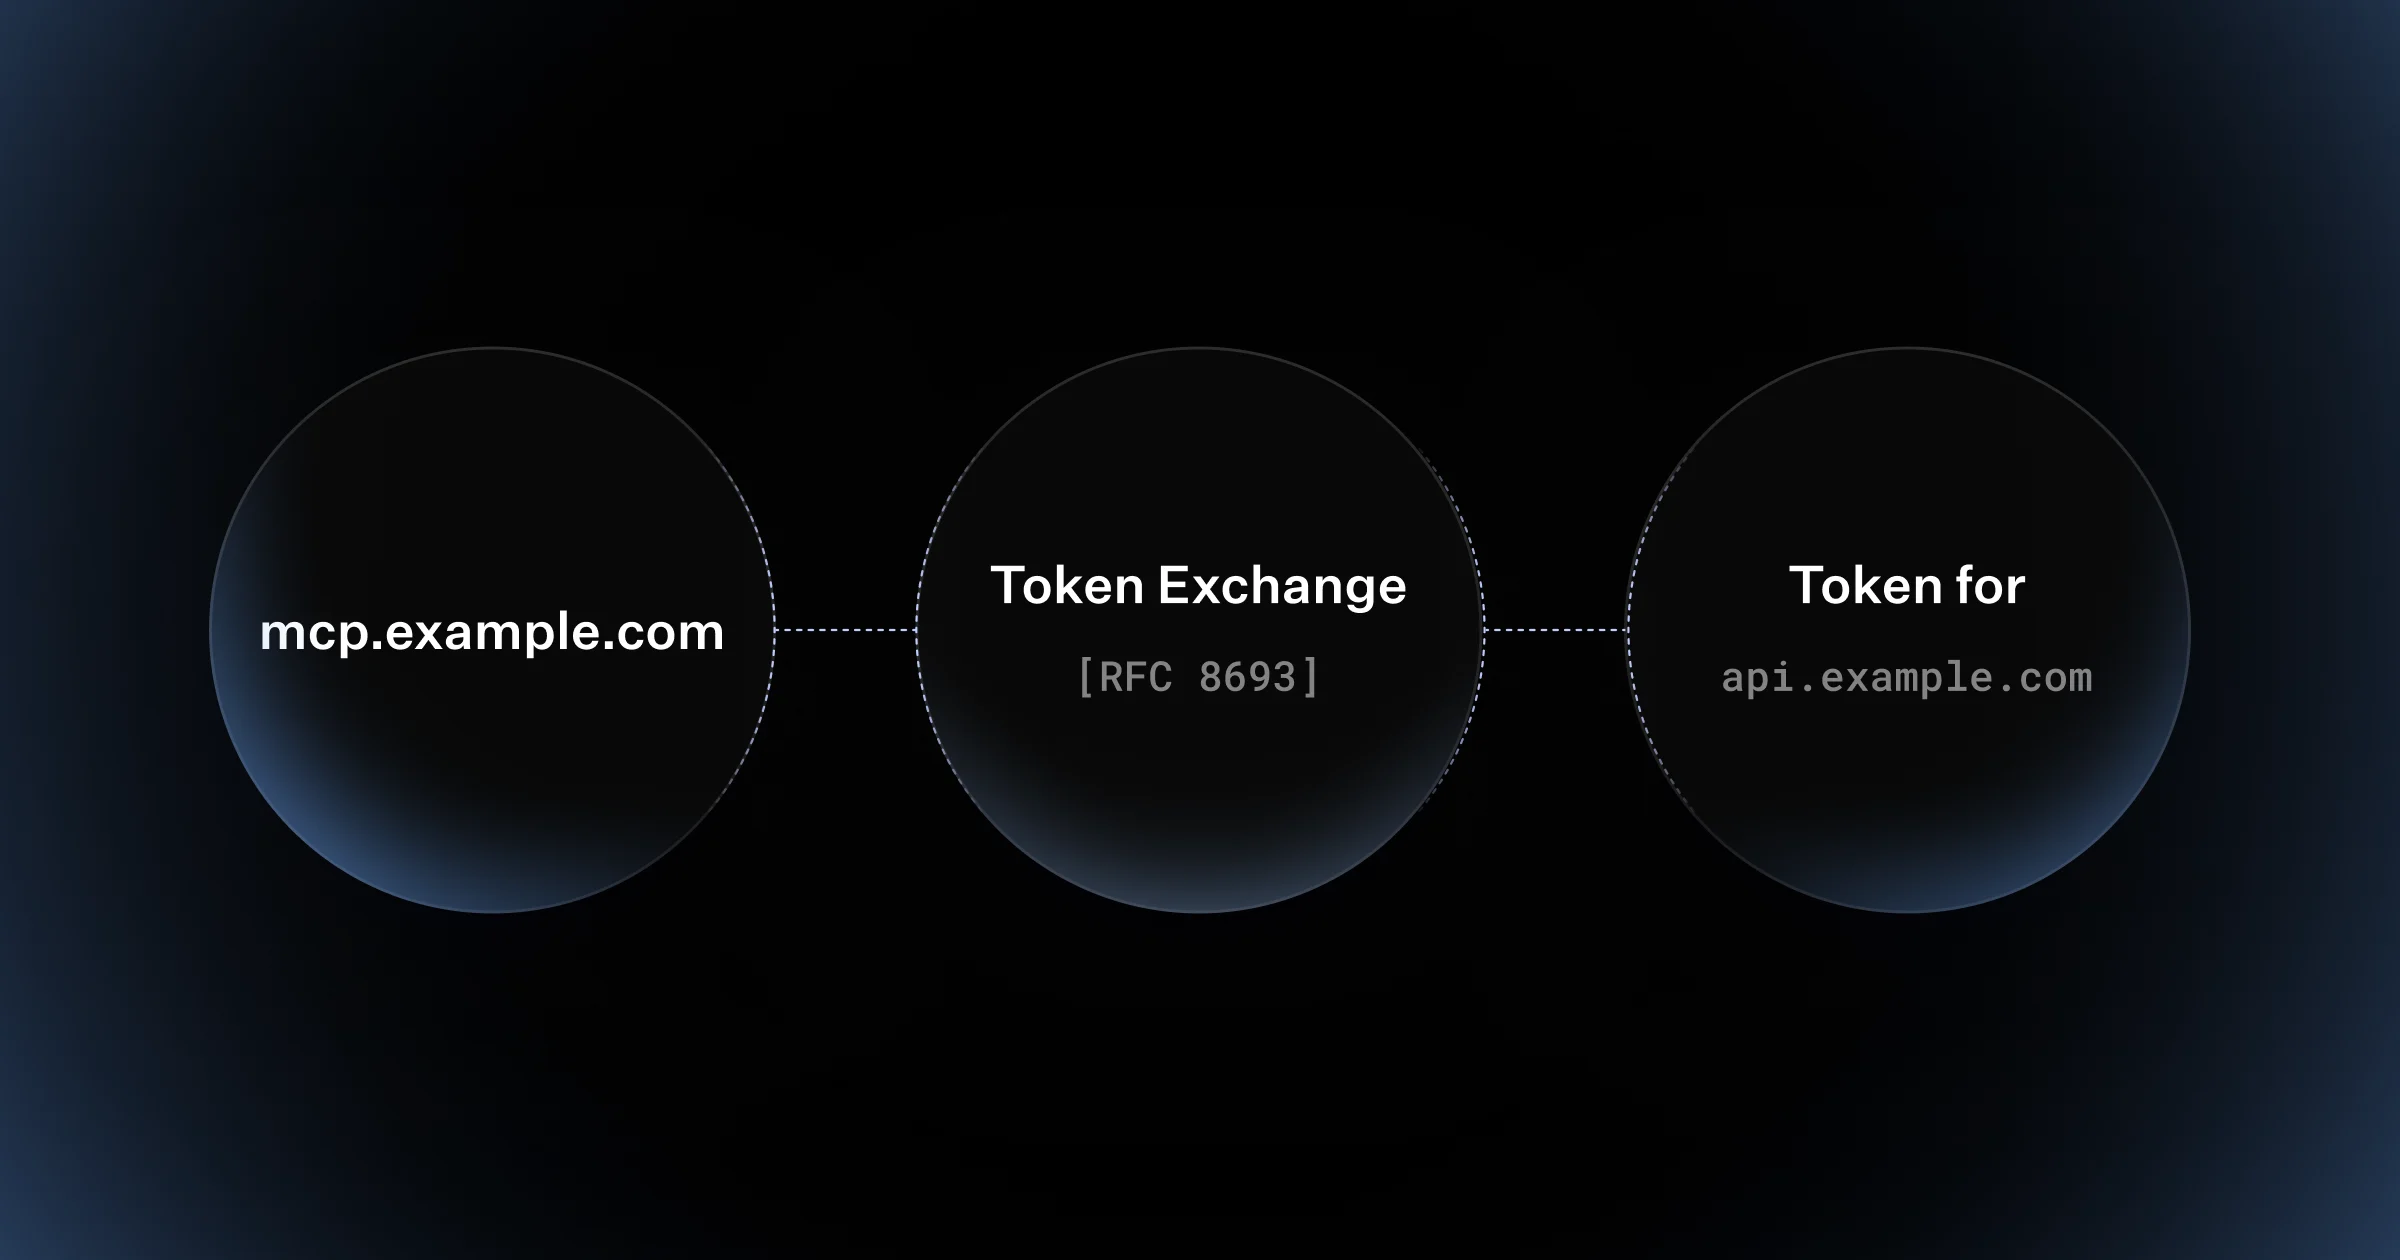
WorkOS Connect now supports token exchange (RFC 8693). A first-party Connect app can exchange an access token issued for one resource for a new token intended for another registered resource. The exchanged token carries forward key claims from the original token, preserving its authorization context, such as a user’s delegation. You can also narrow its scopes to limit access for the downstream service.
For example, your MCP server can exchange a token issued for mcp.example.com for one intended for api.example.com, allowing it to fetch data or perform actions through your API on the user’s behalf.
First-party apps can also introspect tokens issued to public MCP clients in the same environment.
Learn more in the reference guide.