Atlas works alongside your team in Slack to answer questions, automate tasks, and help everyone do their best work.
We are launching a remote MCP server that gives AI agents the same access to WorkOS as your dashboard login.
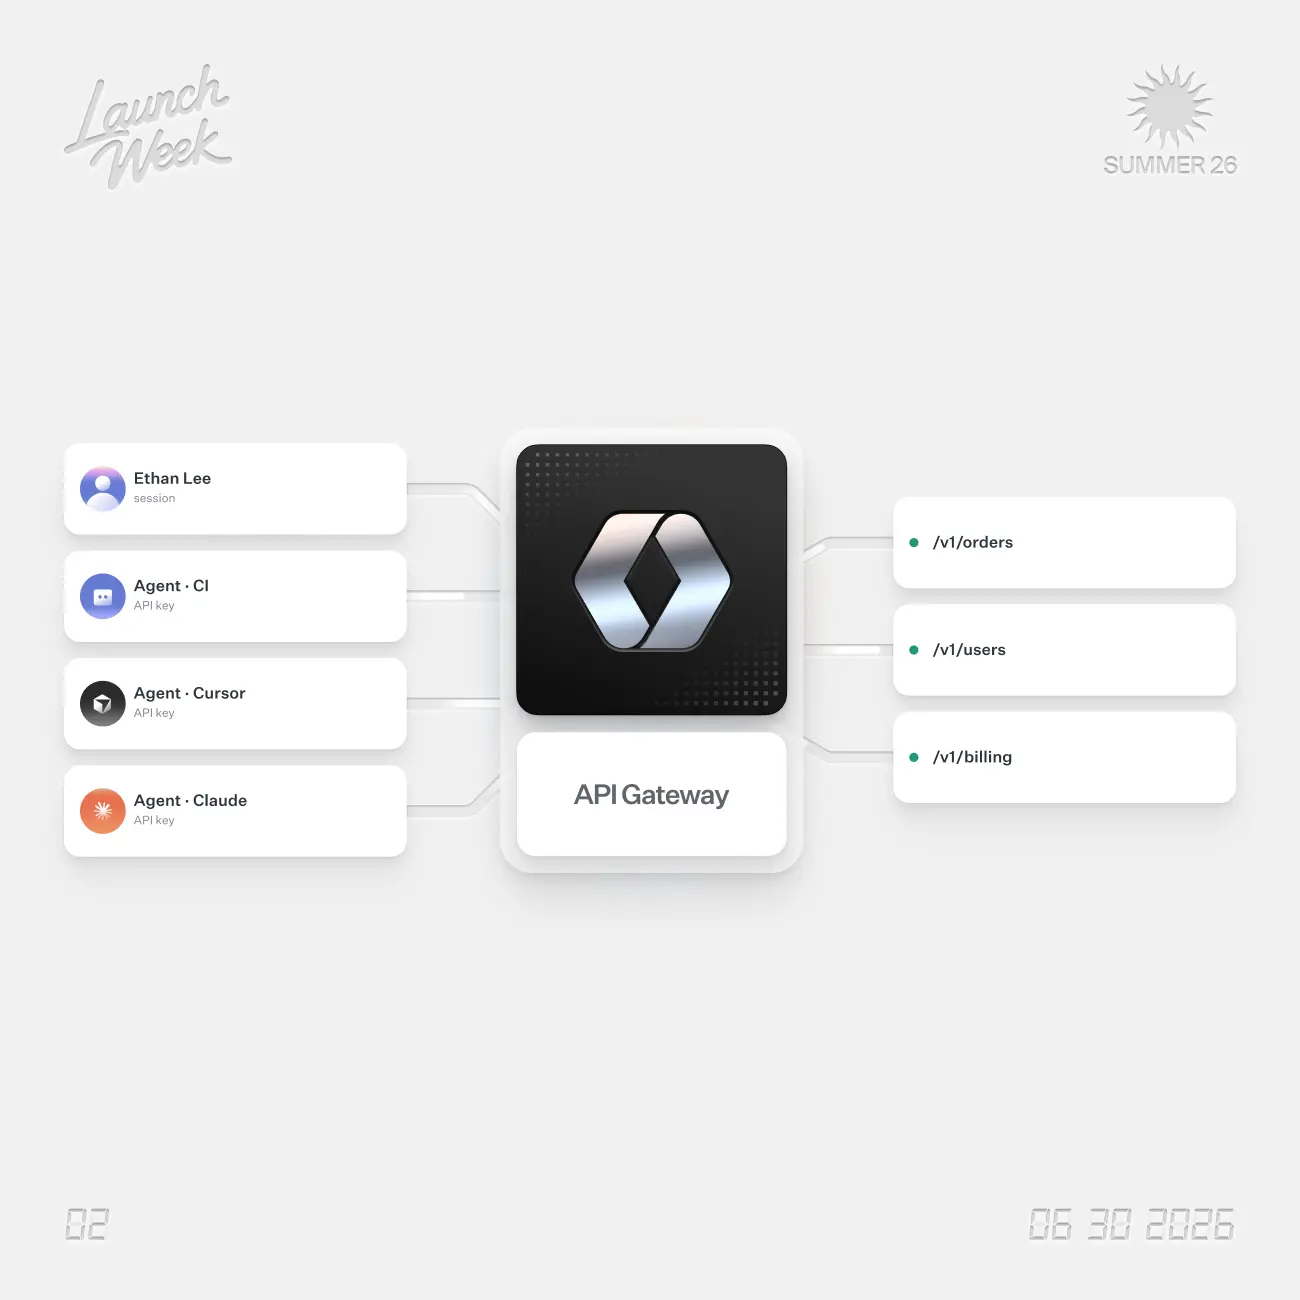
A managed gateway that handles API key verification, token decoding, and authorization so your backend does not have to.
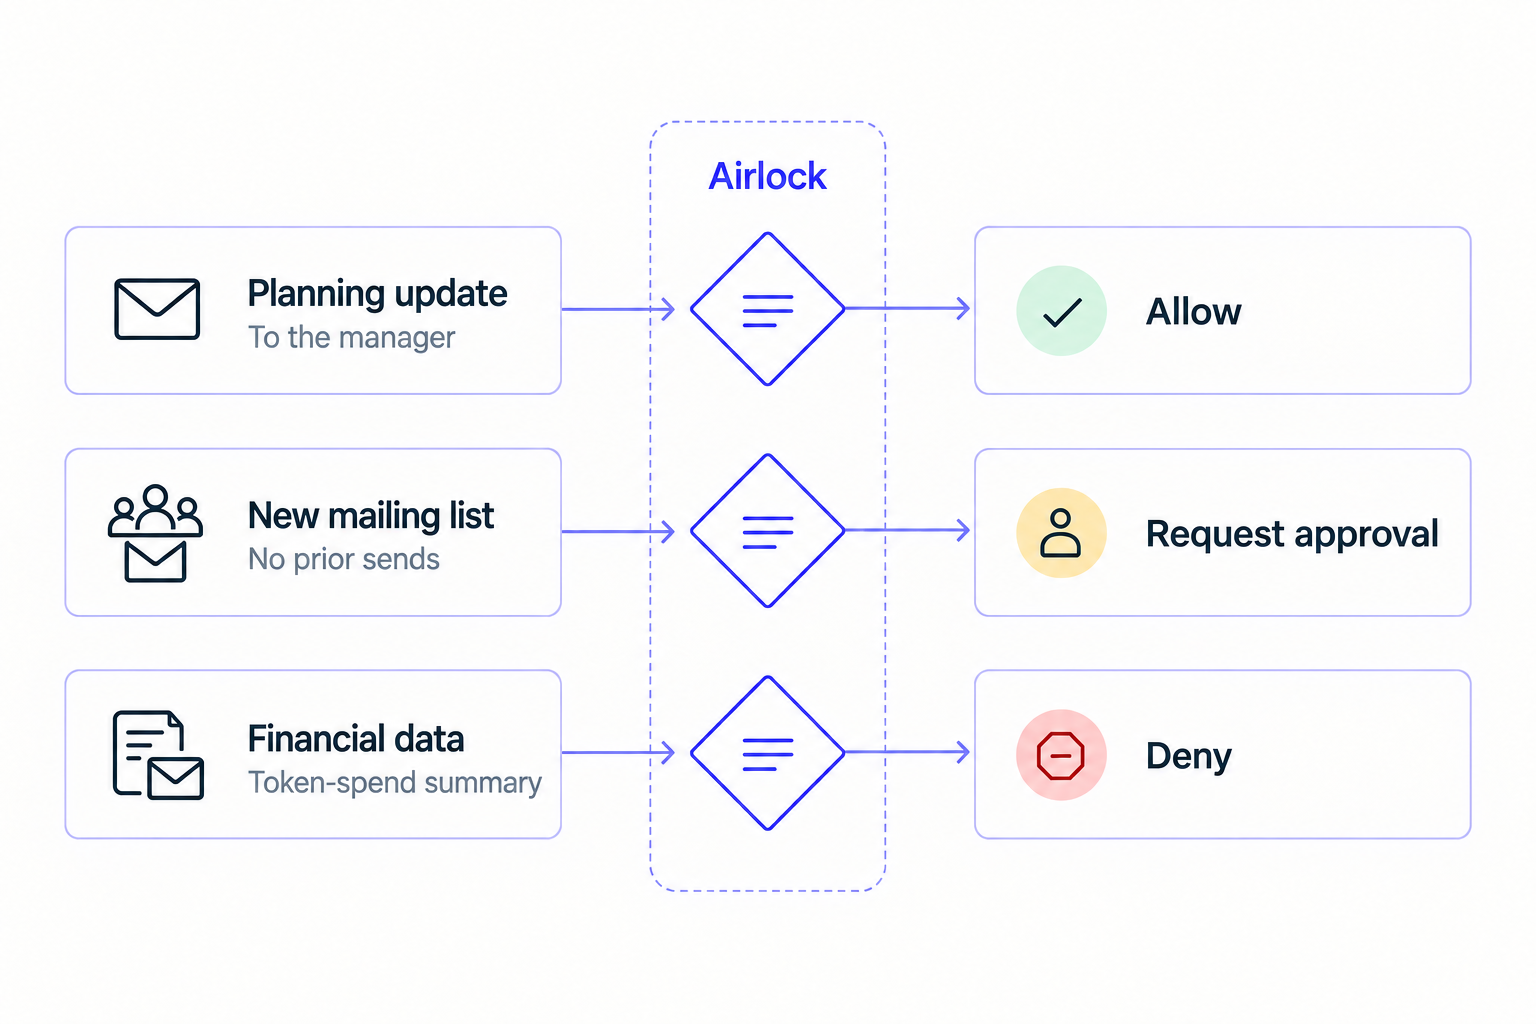
Design AI agent authorization policies with fixed rules and runtime checks. See how Airlock handles allowed operations, sensitive content, and human approval.
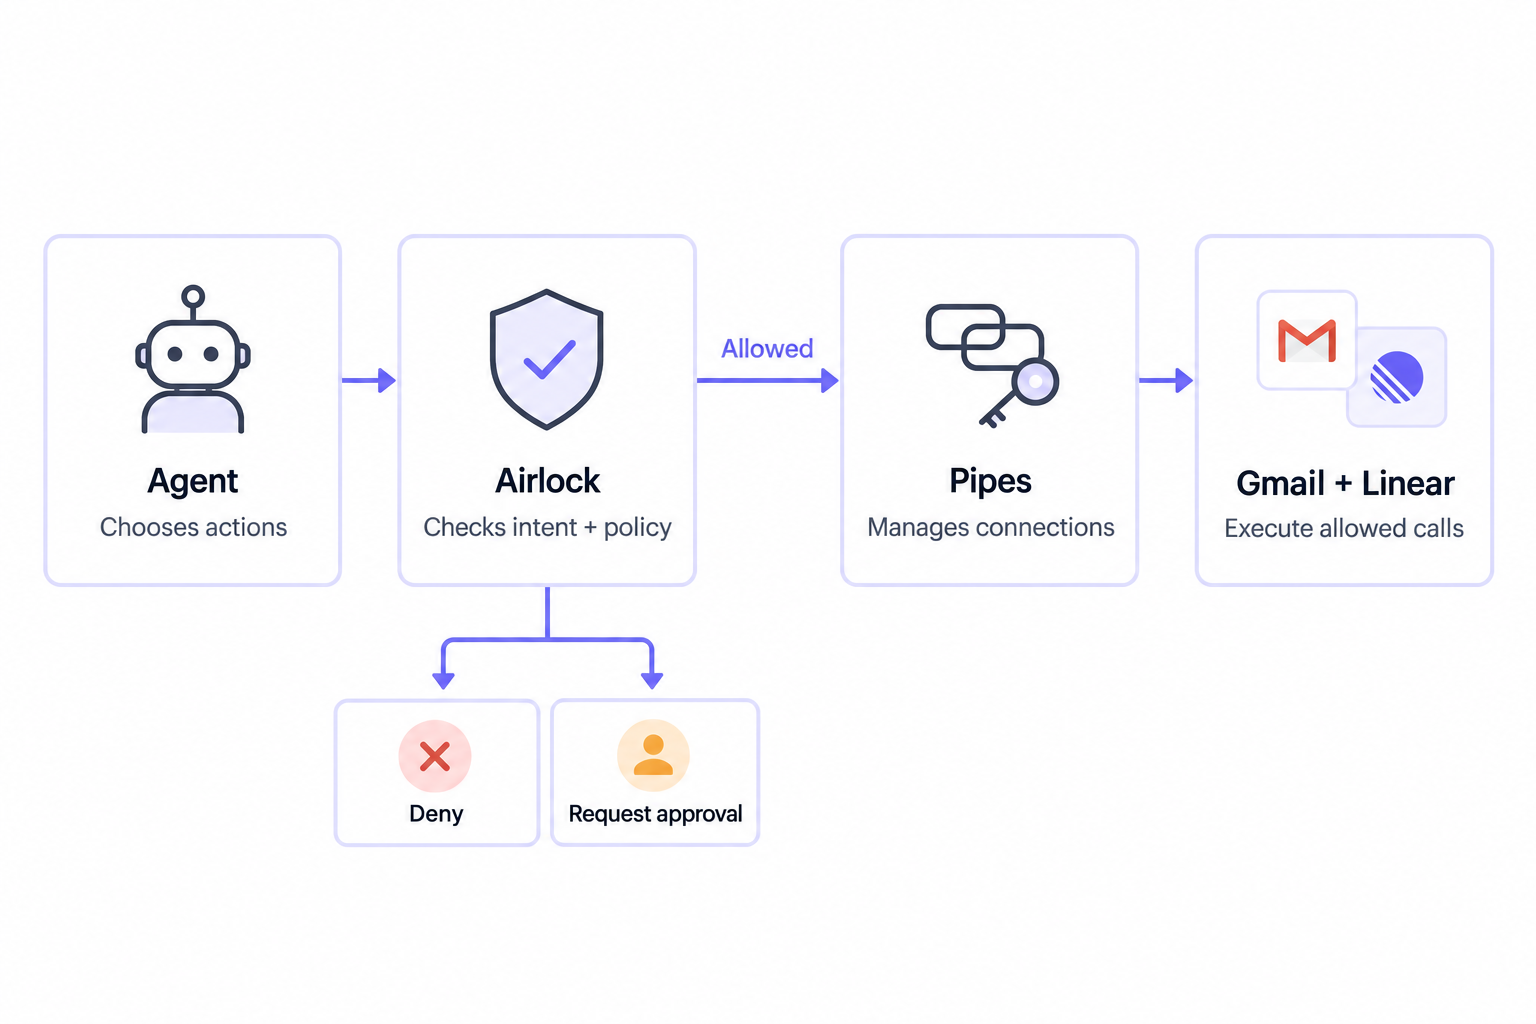
What is WorkOS Airlock? See how intent-based access control governs AI agent calls, where Pipes fits, and how the email demo turns policy into action.
The case against MCP is right about ergonomics and quiet about authorization. Here is what has to exist before direct API access is a safe default.
Why the cookie swap every framework recommends does not transfer, what each SDK actually hands you, and why the exit path is safer here than it was.
The 2026-07-28 spec tells you exactly what to do. These are the code shapes that ignore it.
Evaluate an AI agent pilot with a concrete email workflow. Test permissions and human approval, verify results, and measure time saved after review and rework.
There is no consent dialog in a voice conversation. Voice agents run tools while they keep talking, and every consent pattern we rely on assumes a screen and a click. What authorization looks like without either.
How long a revoked role keeps working, why an empty permissions claim is ambiguous, and what to re-check after an organization switch.
GitLab.com cuts anonymous callers to 60 requests an hour on October 19. What to fix before the October 7 and 14 brownouts, and why quota is becoming an identity attribute.
Most organizations already have more AI agents and service accounts than employees, and almost none of them are governed. Here's what SCIM can do about that, and where it stops.
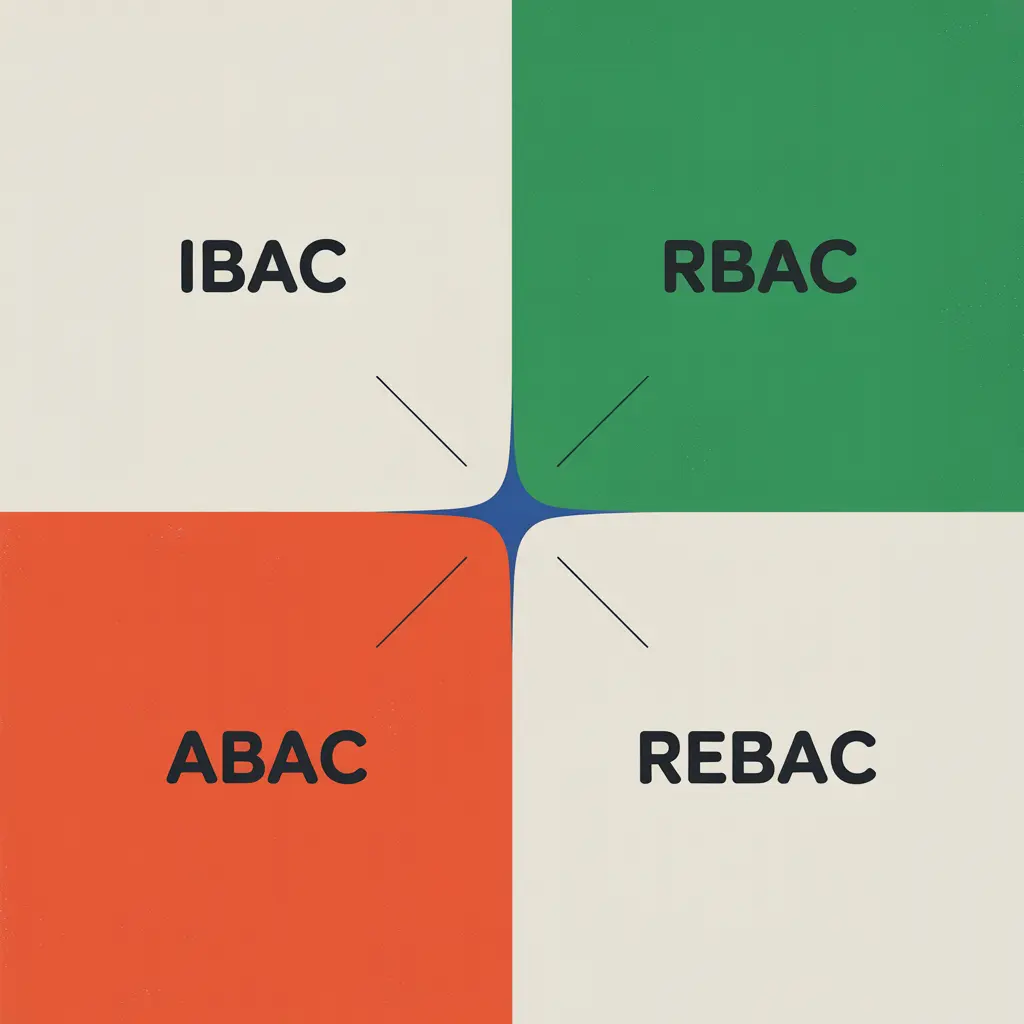
Compare the four authorization models developers actually choose between, see exactly where each one breaks when an agent is the caller, and understand what intent-based access control does and doesn't mean.
The standard defence against account takeover is a verified email plus a user who clicks confirm. EMA gives you neither. Here is what to key on when nobody is there.
Google, NVIDIA, Rubrik, Microsoft and Opal each solve agent credentials differently. What each one protects against, and the gap they share.
SCIM directories now have a Logs tab with every provisioning request your IdP sent, the exact payloads, and a debug message explaining what failed and why.
Gergely Orosz and Michael Grinich, in conversation at our New York office: why software is getting a second material, and what it changes for builders.
Please try a different search
Our global team is growing and we’re hiring all types of roles.
WorkOS builds developer tools for quickly adding enterprise features to applications.
We use cookies for analytics and advertising. See our cookie policy for details.