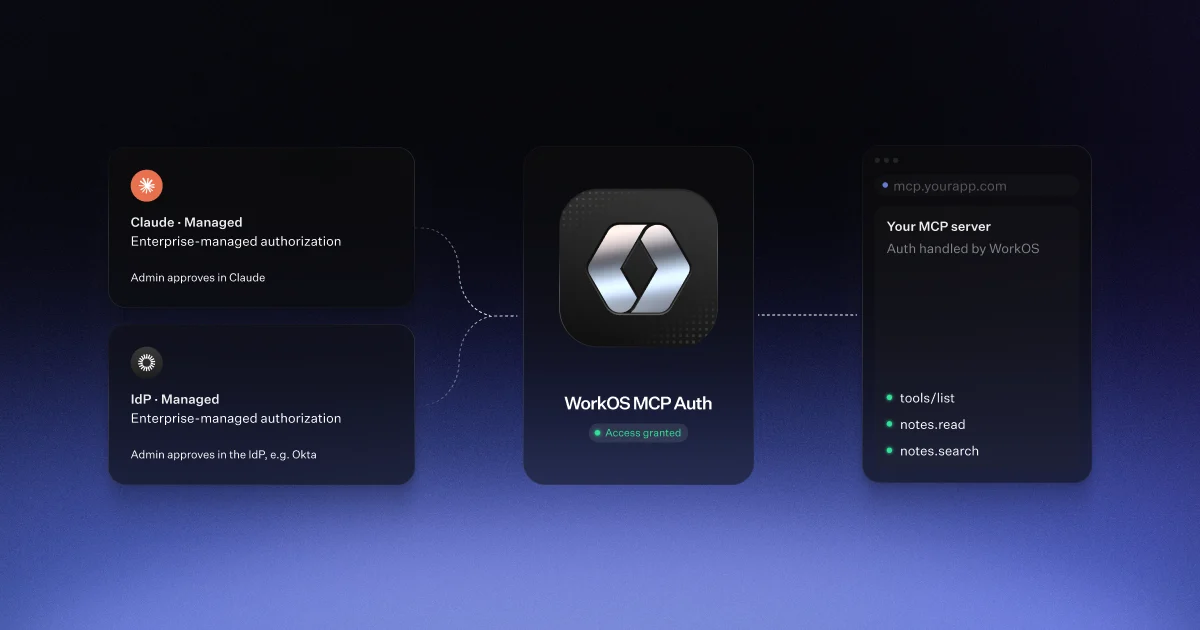
MCP Auth now supports Claude auto-connect, extending Enterprise-Managed Authorization (EMA) to organizations whose identity provider doesn't support Cross App Access (XAA). Instead of the IdP, Claude issues the identity assertion (ID-JAG), and MCP Auth exchanges it for an access token to your MCP server.
Your customers' enterprise admins now have more choice over where they manage MCP access: in their identity provider, or directly in Claude. Either way, they approve your MCP server once, and employees connect from Claude without a separate sign-in or consent screen.
Claude auto-connect is available in early access in MCP Auth. Reach out via email or Slack or read more in the docs.