Atlas works alongside your team in Slack to answer questions, automate tasks, and help everyone do their best work.
We are launching a remote MCP server that gives AI agents the same access to WorkOS as your dashboard login.
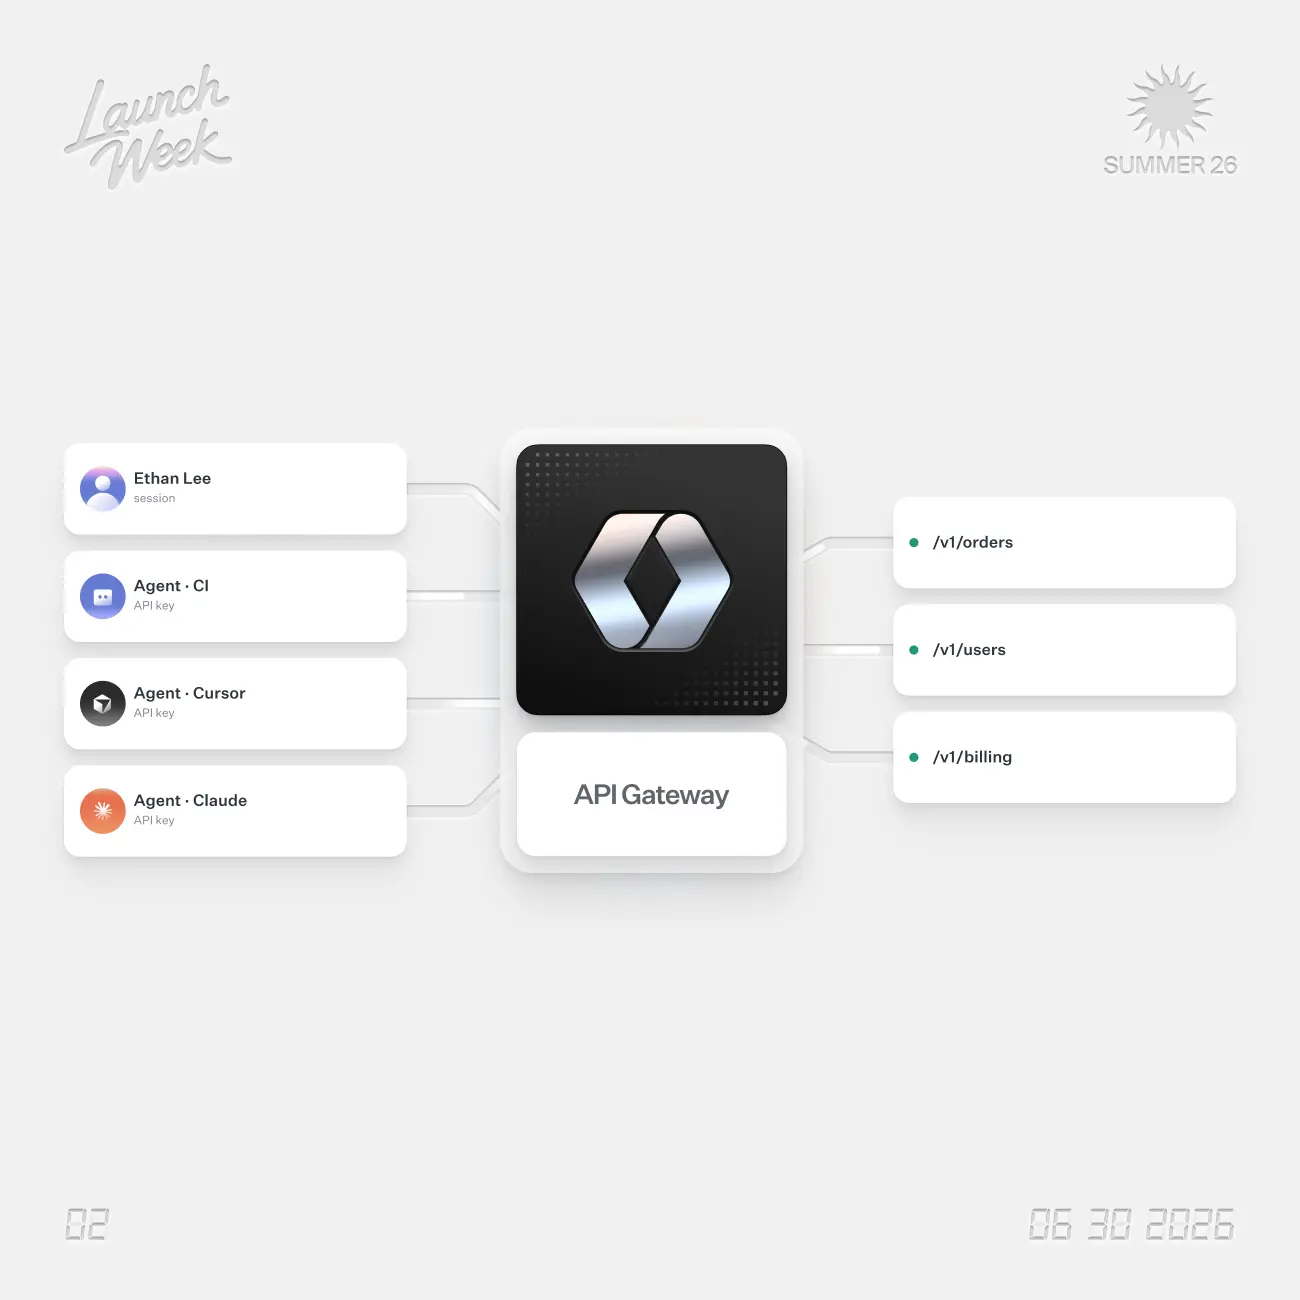
A managed gateway that handles API key verification, token decoding, and authorization so your backend does not have to.
Slack, Notion, and Linear each take a different approach to per-tenant roles and permissions. Here are the patterns worth stealing for your own app.
Master secure authentication in Node.js from Passport.js and JWTs to enterprise SSO, with production-ready patterns and security best practices.
How attackers turn legitimate consent prompts into persistent backdoors, and what your team can do about it.
A deep dive into the FIDO2/WebAuthn protocol mechanics that tie every passkey to a specific domain, making credential theft physically impossible at the cryptographic layer.
What to use when your B2B auth needs outpace PropelAuth.
30 CVEs in 60 days, a backdoored npm package stealing emails, and a hosting platform flaw that put 3,000 servers at risk. Here's how to secure the supply chain your AI agents depend on.
A complete breakdown of one of the most dangerous JWT vulnerabilities, from the cryptographic mechanics to the defensive code patterns that stop it.
Symmetric vs asymmetric JWT signatures: how each algorithm works, when to use which, and the security tradeoffs every developer should know
A 2026 guide to the leading IAM solutions for SaaS teams, with a breakdown of features, pricing, and trade-offs to help you choose the right provider and start closing enterprise deals faster.
Your users enable multi-factor authentication, use strong passwords, and follow every security best practice you recommend. But none of it matters if an attacker is sitting between them and your login page, relaying traffic in real time and walking away with a valid session cookie.
From forged assertions to memory leaks, SAML's XML foundations keep producing serious bugs. Here's what happened and what you should be doing about it.
Most AI agents run with borrowed sessions and far more access than they need. Here's how to replace that with scoped, revocable credentials and tool-level authorization.
Master secure authentication in Laravel from Breeze and Sanctum to enterprise SSO, with production-ready patterns and security best practices.
API keys, token files, OAuth Device Flow, and Client Credentials compared. A practical guide to choosing the right authentication pattern for your CLI.
How FIDO2 and passkeys use cryptographic domain binding to stop phishing attacks, why SMS and push notification fallbacks destroy your security posture, and what to do about it.
Please try a different search
Our global team is growing and we’re hiring all types of roles.
WorkOS builds developer tools for quickly adding enterprise features to applications.
We use cookies for analytics and advertising. See our cookie policy for details.